Tag: spf dkim dmarc

  • How to Reduce Email Bounce Rate the Smart Way

    How to Reduce Email Bounce Rate the Smart Way

    In a 2025 B2B cold email dataset covering 7.5 million emails, 128,605 messages bounced, creating a 1.71% bounce rate and an implied 98.29% deliverability rate. That result reframes how to reduce email bounce rate: verification matters, but it isn't the whole job. A bounce spike can come from invalid addresses, temporary mailbox failures, authentication gaps, inconsistent volume, or provider throttling.

    The practical approach is diagnostic first. Measure the failure type before cleaning the list, authenticate before increasing volume, and suppress recipients according to the SMTP response rather than a generic platform label. For most B2B programs, a bounce rate below 2% is a healthy operating target, while rates from 2% to 5% deserve investigation and anything above 5% indicates serious risk, as summarized by Belkins' email deliverability benchmarks.

    Why Email Bounce Rate Is Quietly Costing You

    A single percentage point of bounces represents more than undelivered messages. It means sending capacity was used on addresses that produced no conversation, sales staff may still work dead records, and mailbox providers receive another signal about the quality of your traffic. Over time, repeated failures can weaken inbox placement at Gmail, Microsoft, and Yahoo, even when your copy and offer are strong.

    The damage often remains invisible until inbox placement falls sharply. Teams see a campaign report, notice fewer replies, and blame subject lines or timing. By then, domain reputation may have been deteriorating across several sends. A high bounce rate can also distort campaign analysis because delivered and undelivered recipients are evaluated together.

    Practical rule: Treat bounce rate as an operating control, not a post-campaign vanity metric.

    The financial cost is easy to overlook:

    • Wasted sending capacity: A bounced message consumes campaign resources without creating an opportunity.
    • Sales time on dead records: Reps may research, sequence, and follow up with contacts who can never receive the message.
    • Reputation pressure: Providers can interpret recurring delivery failures as evidence of poor list quality or risky sending behavior.
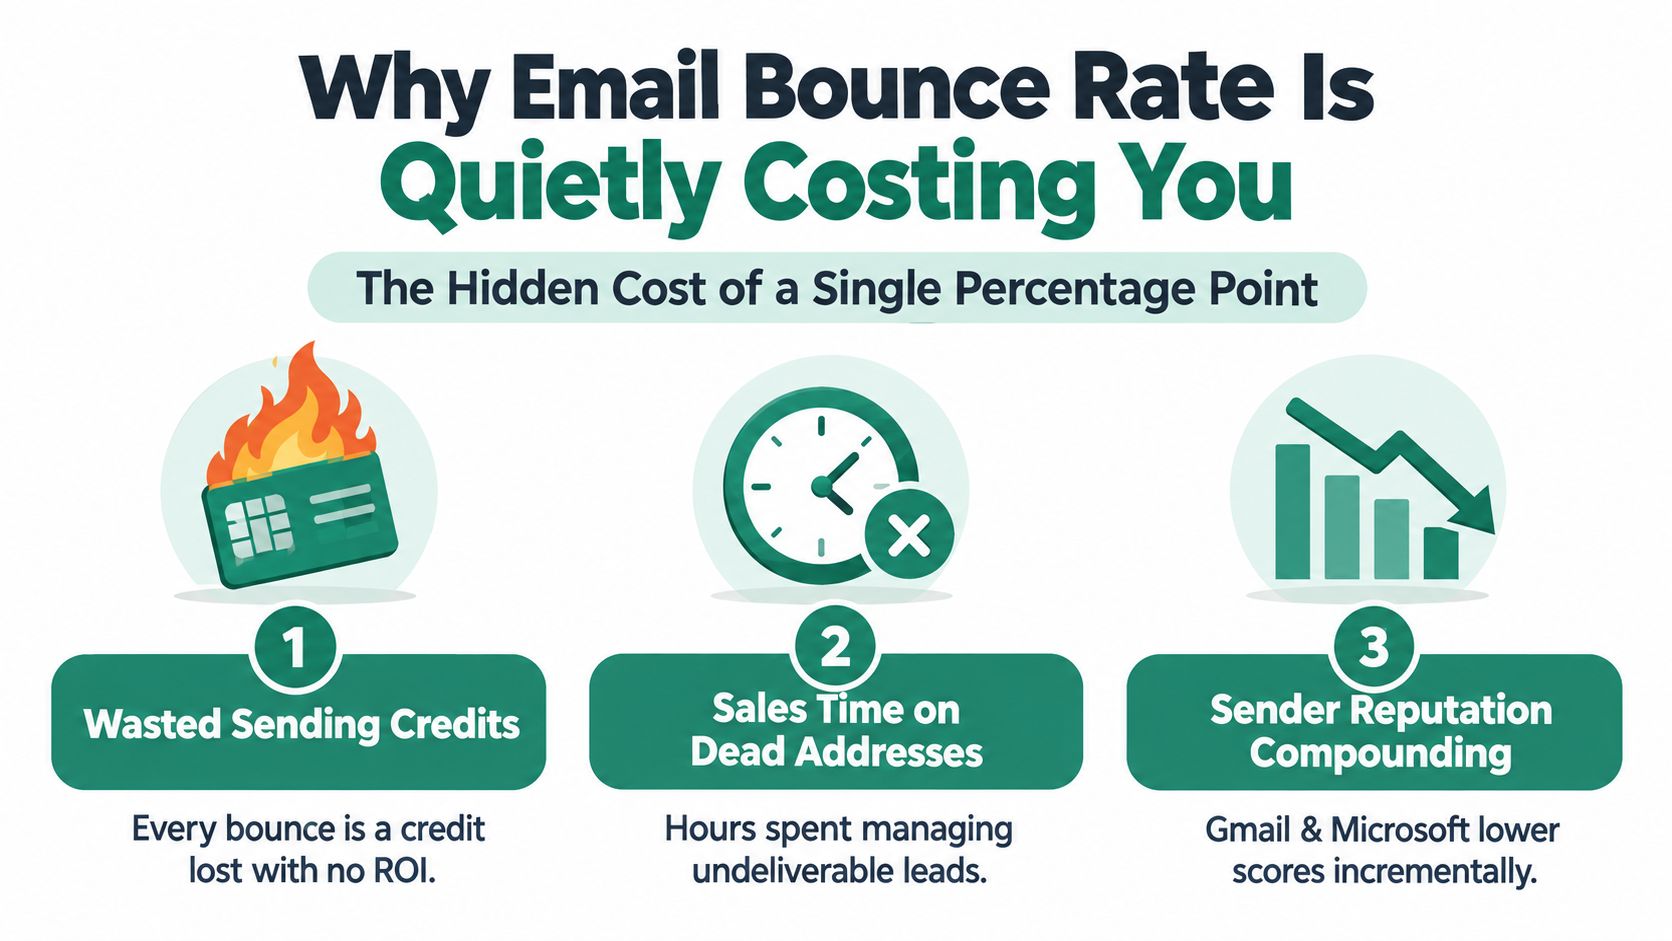
    An infographic showing three hidden costs of high email bounce rates including wasted credits and reputation damage.

    Start with a baseline from the same sending stream, domain, and recipient mix. Don't combine transactional, newsletter, and cold outreach results into one number if their delivery conditions differ. Review the SMTP response, provider, sending time, and authentication result alongside the aggregate rate.

    The goal is straightforward: keep total bounces below 2%, remove permanent failures immediately, and prevent authentication or sending-pattern problems from creating avoidable temporary failures. The exact hard-bounce threshold should be defined from your own historical data and provider feedback, not invented as a universal benchmark.

    Understanding Bounce Types and What a Healthy Rate Looks Like

    A bounce spike is easier to fix when you separate three events that sending platforms often combine. A hard bounce means the address has failed permanently, such as an unknown user or nonexistent mailbox. A soft bounce is usually temporary, caused by a full mailbox, transient server error, or greylisting. Provider throttling is different: the receiving platform delays acceptance because it questions your volume, cadence, reputation, or authentication.

    Read the SMTP response before choosing a remedy. 550 user unknown usually identifies a bad address. 4.2.1 points to a temporary mailbox condition. 4.7.1 can indicate throttling or a provider policy decision, so deleting the recipient will not repair the sending system.

    Bounce Category What It Means Example SMTP Code Target Rate
    Hard bounce Permanent address failure 550 user unknown or 5.1.1 Keep below your internal hard-bounce ceiling and suppress immediately
    Soft bounce Temporary delivery problem 4.2.1 or 4.4.1 Keep low through verification and controlled retries
    Provider throttling Receiving provider delays acceptance 4.7.1 Diagnose volume, reputation, and authentication before retrying

    Use under 2% total bounce rate as a broad operating reference. Rates between 2% and 5% indicate a warning zone, while rates above 5% carry high deliverability risk, according to the Belkins deliverability analysis. That analysis also reports a 1.71% overall bounce rate for a 2025 B2B dataset, which illustrates a low-bounce program rather than a guarantee for every sender.

    Cloudflare documents a hard-bounce target below 2% and delivery rates above 95% in its email deliverability guidance. Use those figures as health checks, then investigate the events behind your own rate.

    Read the failure before choosing the remedy

    Put hard bounces on permanent suppression lists immediately. Apply controlled retries to soft bounces, then review repeated failures. For provider throttling, adjust volume or cadence and check reputation and authentication while keeping the address eligible for later delivery.

    A campaign dominated by hard bounces has a data problem. A campaign producing repeated 4.7.1 responses may have an infrastructure problem. Treating both as list-cleaning tasks wastes time and leaves the cause untouched. The bounce category should determine whether you suppress, retry, or repair the sending setup.

    Building a Clean List Before You Press Send

    List hygiene works best as a continuous control with three layers. The first layer operates when a person submits an address. The second confirms that the person controls the mailbox. The third checks whether older records are still usable before a campaign begins.

    Layer one starts at capture

    Add real-time validation to forms, imports, and CRM workflows. The check should catch syntax errors, suspicious domains, disposable providers, and addresses that fail domain or mailbox verification. If a B2B SaaS visitor types name@gmial.com, the form should identify the likely typo before the record enters the database.

    Role addresses need a policy rather than an automatic assumption. info@, admin@, and support@ may be valid operational inboxes, but they often create shared ownership and lower response quality. Decide whether your campaign is intended for named decision-makers, then block or route role-based records accordingly.

    For teams that collect prospects from multiple sources, EmailScout's clean email list workflow can be considered alongside other verification and CRM processes. The important control is the timing. Verification performed after a bad record has already entered several audiences is less effective than rejecting it at capture.

    Layer two confirms intent

    Use double opt-in for newsletter subscriptions, gated resources, event registrations, and other permission-based acquisition. The confirmation message filters typographical errors and fake signups, while also giving the recipient a clear record of consent.

    Double opt-in has a trade-off. Some legitimate people won't complete the confirmation step, so the list may grow more slowly. That reduction in volume is usually preferable to accepting addresses that are mistyped, abandoned, or collected without meaningful intent.
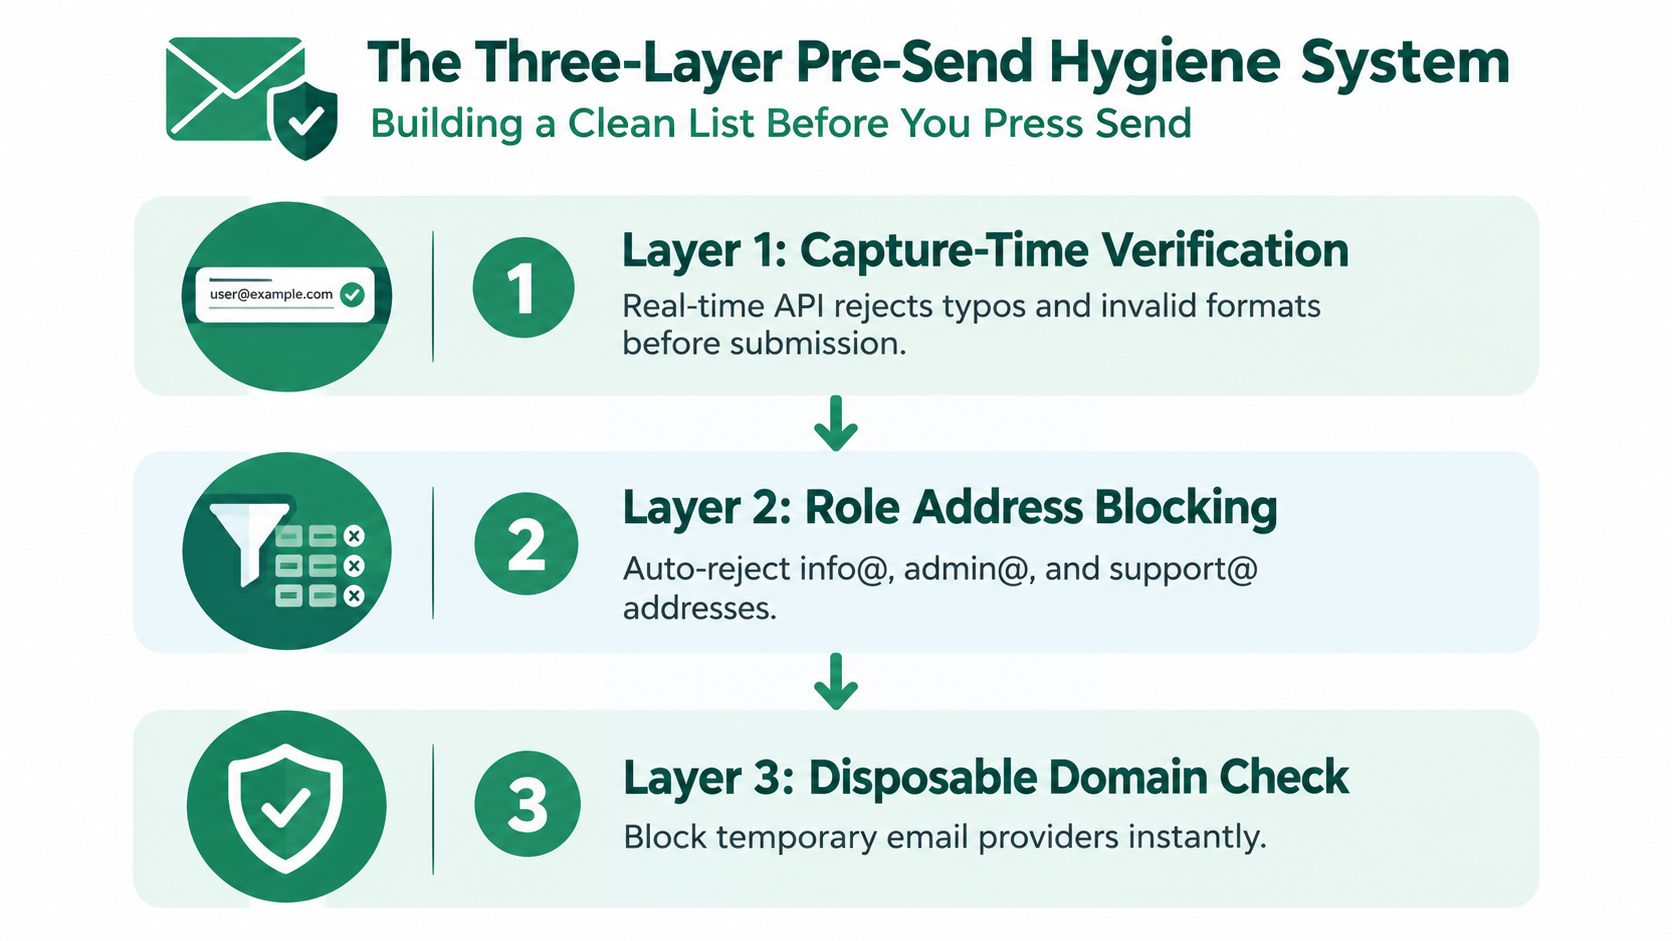
    A diagram illustrating a three-layer pre-send hygiene system to ensure a clean email marketing list.

    Layer three checks for decay

    Re-verify older records before each significant campaign, especially when the data has been sitting for 30 days or more, a timing recommendation discussed in guidance on email verification and bounce prevention. People change employers, domains stop resolving, and mailboxes are deactivated. A list that was acceptable when collected may not be safe to send today.

    Separate verified, risky, unknown, and suppressed records. Don't mix them into one audience because a single aggregate rate can hide a deteriorating segment. A quarterly list that has aged beyond a campaign cycle should be checked again before re-engagement, rather than sent in full and cleaned afterward.

    Setting Up SPF, DKIM, and DMARC the Right Way

    Authentication won't repair a bad list, but missing or misaligned authentication can make a clean list look suspicious. Configure the controls in order, document every sending service, and test the live result rather than trusting a setup screen.

    SPF comes first

    Publish an SPF TXT record that names every authorized sending source for the domain. Keep the record within the DNS lookup limit, and avoid permissive mechanisms such as +all or ?all. An incomplete SPF record can cause legitimate messages to fail, while an overly broad one weakens the control.

    Check the published record with a DNS lookup tool or MXToolbox. Compare the result with your actual ESP, CRM, transactional service, and support platform. Remove services that no longer send, because stale authorization creates both operational confusion and unnecessary exposure.

    DKIM proves message integrity

    Create a separate DKIM selector for each sending service, publish its public key, and enable the selector inside the provider. Send a test message and inspect the authentication results, not just the provider's green status indicator.

    A common failure is a selector that exists in DNS but isn't enabled for the stream using it. Another is reusing one key across unrelated services without a clear rotation and ownership process. Keep a record of selectors, responsible teams, and the systems that depend on them.

    DMARC gives receivers instructions

    Start DMARC with a reporting-only policy so you can identify unauthorized sources and alignment failures. Send aggregate reports to a mailbox that someone actively reviews, then move toward enforcement after the legitimate streams pass consistently. Machine Marketing's guidance on reputation management for industrial marketers provides useful context for treating authentication and sender reputation as an ongoing operational discipline.

    Protocol DNS Record Type Where to Publish Most Common Mistake How to Verify
    SPF TXT Root sending domain Missing a legitimate sender or using an unsafe mechanism DNS lookup or MXToolbox
    DKIM TXT Selector subdomain Publishing a key without enabling the selector in the ESP Test message authentication headers
    DMARC TXT DMARC subdomain Enforcing before alignment is understood Aggregate reports and provider tools

    Use EmailScout's SPF, DKIM, and DMARC explanation as a reference when documenting the records for sales and marketing teams. Authentication should be rechecked whenever a new platform is introduced, a domain changes, or an existing sender is retired.

    A Real Bounce Rate Rescue Story and the Four Fixes Behind It

    A 2026 case study from Bulk Email Checker describes a B2B SaaS company that reduced its bounce rate from 14.2% to 0.6% in 30 days. The reported result followed several changes at once, including bulk verification, real-time form validation, engagement-based suppression, and SPF, DKIM, and DMARC corrections, as documented in the B2B SaaS bounce-rate case study.

    That story matters because the team didn't treat the problem as a single bad export. A rate that high can reflect several failures operating together. The reported reduction was 13.6 percentage points, or roughly a 95.8% relative improvement, but the case shouldn't be read as a promise. It shows how much preventable failure can sit inside list quality and sending infrastructure.

    The sequence is more useful than the headline:

    1. Validate the existing database. The team performed bulk verification and removed addresses that couldn't be trusted before another send.
    2. Validate at capture. New form submissions were checked immediately, preventing the repaired list from decaying through fresh typos and invalid records.
    3. Suppress by engagement. Recipients with repeated delivery or engagement problems were excluded rather than repeatedly retried.
    4. Repair authentication. SPF, DKIM, and DMARC were corrected so receiving providers could evaluate the sender with stronger identity signals.
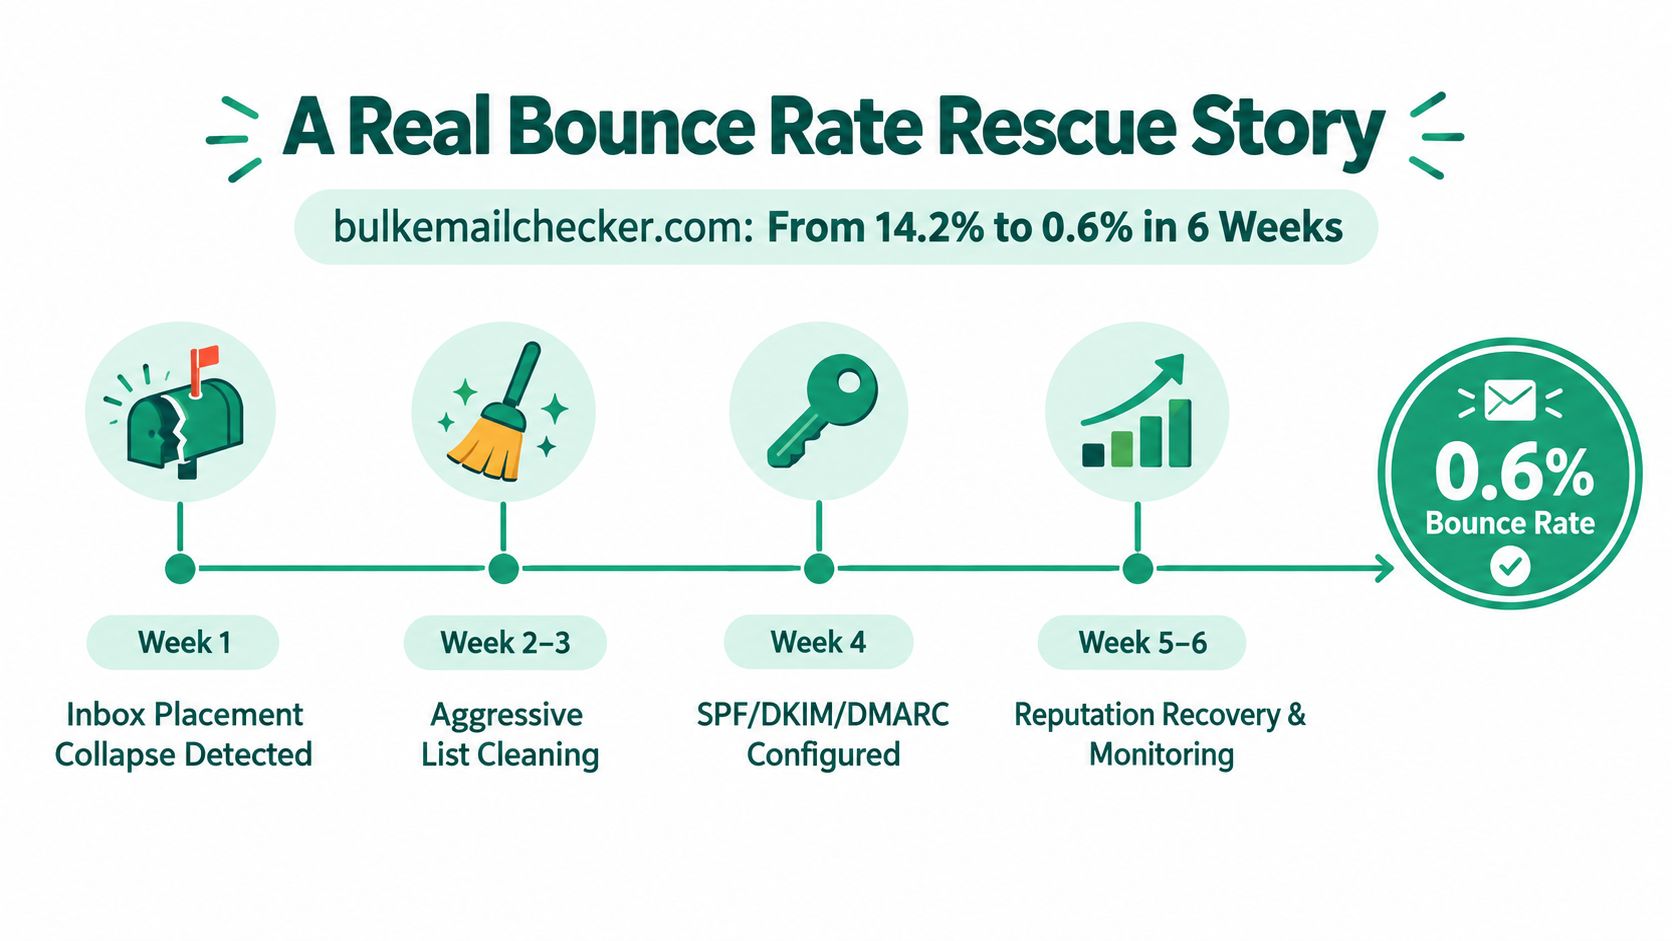
    A timeline graphic showing the steps taken to reduce email bounce rate from 14.2% to 0.6%.

    The lesson is to avoid copying a single tactic and expecting the same outcome. Verification removes address-level risk, suppression prevents repeated damage, and authentication improves the receiving system's confidence in the sender. If the response codes show throttling, add controlled volume and cadence changes instead of deleting valid recipients.

    Reading Bounce Codes and Suppressing the Right Addresses

    Your bounce log should answer two questions: Can this address ever receive mail? and Why did this attempt fail now? The first question determines suppression. The second determines whether the sender, message, or provider needs attention.

    Permanent failures such as 5.1.1, 550 user unknown, or mailbox-not-found responses should move directly to permanent suppression. Don't retry them through another campaign or allow CRM synchronization to re-add them. A suppression record should survive list exports, audience rebuilds, and provider migrations.

    Temporary responses require more nuance:

    • 4.2.1 mailbox full: Allow a controlled retry window, then suppress after repeated consecutive failures.
    • 4.4.1 temporary failure: Retry while checking whether the same domain is failing broadly.
    • 4.7.1 throttling or policy response: Reduce volume and inspect reputation, authentication, cadence, and refusal text before retrying.
    • 5.7.1 content or policy rejection: Investigate the message, links, and sending identity. The address may still be valid.

    Read the exact refusal text. A platform's “soft bounce” label can hide a provider defense mechanism.

    Build the mapping from raw ESP events, Postfix or equivalent mail logs, and Gmail Postmaster data where available. Then send the result to an automated suppression service through webhooks or a scheduled CSV process. The automation should distinguish recipient-level failures from domain-level patterns, because suppressing every address at a throttled domain can destroy a valid audience.

    SMTP Code Meaning Category Suppression Action
    5.1.1 User unknown or mailbox unavailable Hard bounce Permanent suppression
    550 Permanent recipient refusal Hard bounce Permanent suppression
    4.2.1 Mailbox full or temporary mailbox issue Soft bounce Retry, then suppress after repeated failures
    4.4.1 Temporary routing or server failure Soft bounce Retry while monitoring the domain
    4.7.1 Throttling or policy-related deferral Provider throttle Cap volume and investigate sender signals
    5.7.1 Message, policy, or content rejection Policy failure Review content and authentication, don't automatically suppress

    A dedicated email scrubbing service can support the address-validation part of this workflow, but no verifier can diagnose every provider-level throttle. Keep SMTP evidence attached to each event so your operations team can see whether the remedy belongs in the list, the message, or the sending infrastructure.

    A 90-Day Bounce Reduction Plan You Can Actually Run

    A durable bounce reduction program treats each spike as an infrastructure diagnosis. Separate hard bounces, soft bounces, and provider throttling before changing the list. A permanent recipient failure needs suppression, while a temporary domain refusal may require lower volume, corrected authentication, or a pause. The operating cycle should connect contact data, DNS, message headers, sending behavior, and event monitoring.

    Days 1 to 30 focus on control

    Start with a full list audit. Remove permanent failures, isolate unverified or risky records, and pause large sends until the results are clear. Check SPF, DKIM, and DMARC for every active sending source, then compare the live DNS records with the authentication results in message headers. A clean list cannot compensate for a misconfigured sender.

    Days 31 to 60 add prevention

    Add real-time validation to forms and imports. Use double opt-in when the consent and quality gains justify the added friction. Define separate suppression rules for recipient failures, repeated mailbox problems, and provider throttling. Do not suppress an entire domain because one provider is temporarily limiting delivery.

    Use re-engagement selectively. Continuing to mail every inactive record keeps low-value addresses in circulation and can increase exposure without improving list quality. Set a clear stopping condition based on engagement and delivery behavior.

    Days 61 to 90 make the system self-protecting

    Set a consistent warm-up and volume pattern for new domains or streams. Review bounce events weekly, then create an automation trigger that pauses or limits sending when the overall rate reaches your internal review threshold. The threshold should reflect your provider mix, historical baseline, and the type of failures observed, rather than a universal number.

    Track two weekly metrics:

    • Hard bounce rate per send: Shows whether capture, verification, and suppression are working.
    • Authentication pass rate: Shows whether legitimate mail is being recognized as authorized.

    Force a full re-validation when a stable segment shows a sudden spike, a domain produces repeated temporary failures, or authentication results change unexpectedly. Base the trigger on the failure pattern and refusal text, not only a dashboard color.
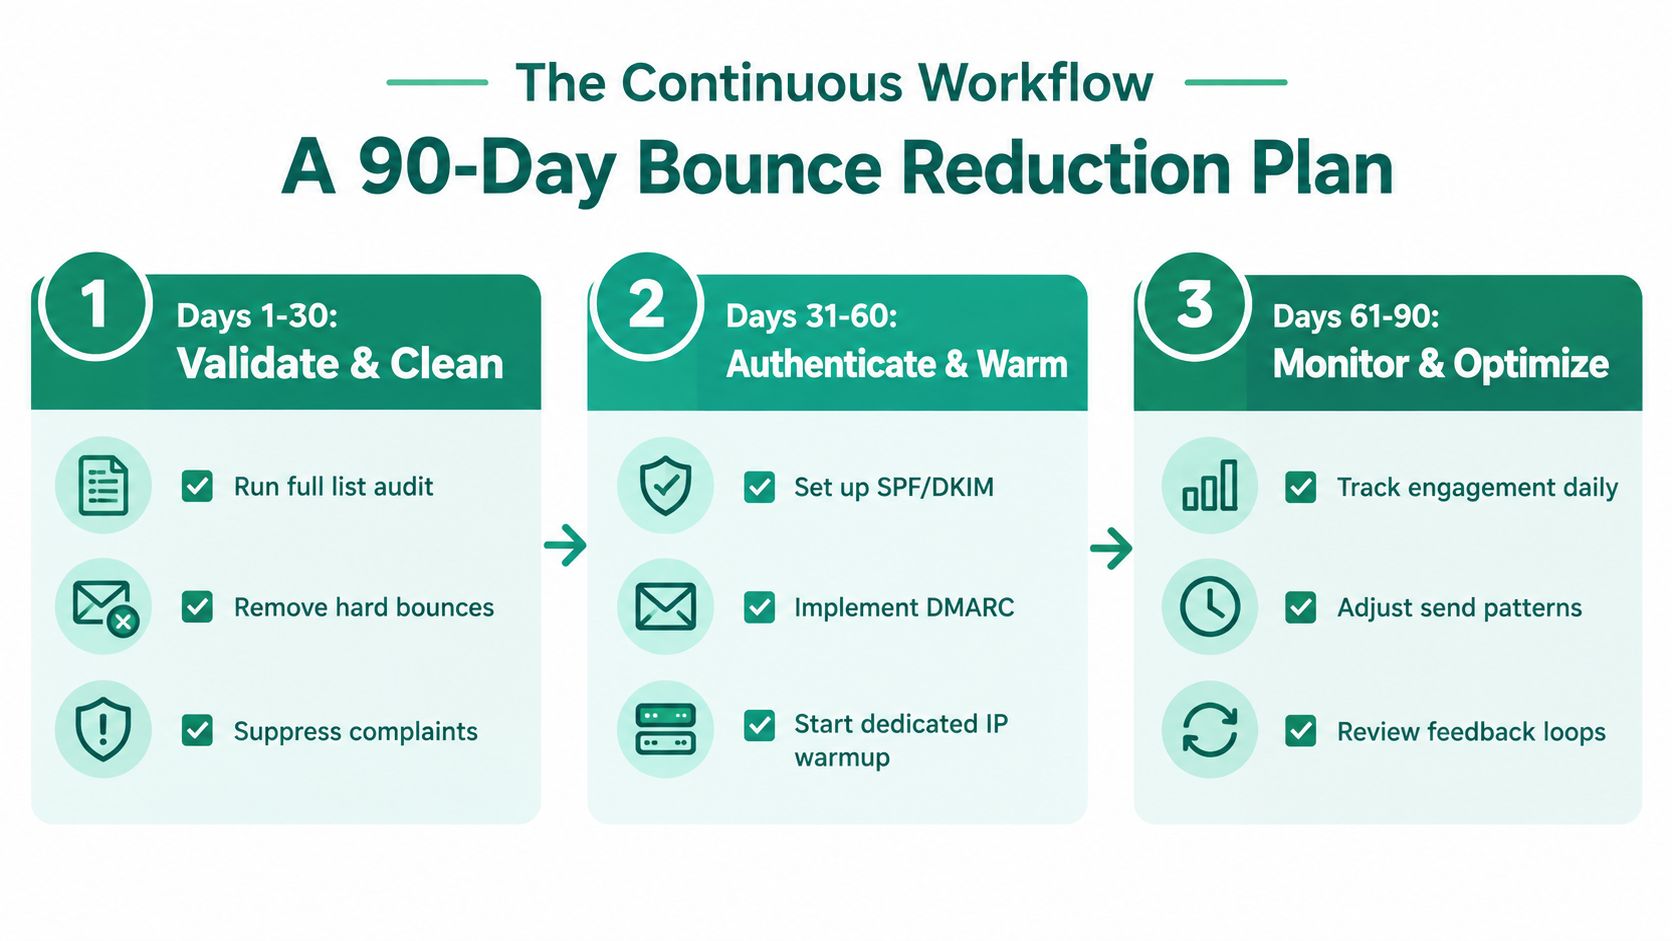
    A 90-day email bounce reduction plan infographic outlining steps for cleaning, authenticating, and optimizing email lists.

    Teams documenting AI-assisted research and outreach workflows can find additional process ideas in a privacy-first ChatGPT alternative blog. Keep deliverability decisions tied to verified SMTP events and your own sending data.

    The result comes from repeated execution: clean capture, accurate suppression, authenticated sending, controlled volume, and review of provider responses. A spreadsheet cleanup starts the process. Monitoring and automatic safeguards keep it working.

    EmailScout helps sales and marketing teams find and verify professional email addresses, clean existing lists, and identify records that may fail before outreach begins. Visit EmailScout to review its verification and list-cleaning workflows, then apply the results to a suppression process that protects your bounce rate.
  • How to Prevent Email Spoofing with SPF, DKIM, and DMARC

    How to Prevent Email Spoofing with SPF, DKIM, and DMARC

    Only 12.8% of domains in a 2026 scan enforced a DMARC policy that blocks spoofed messages, even though 30.4% had published a DMARC record. SPF appeared on 56.0% of domains, which means many organizations have started authentication but still haven't finished the job of stopping forged mail. (2026 email authentication research)

    That gap defines how to prevent email spoofing in practice. Publishing SPF, DKIM, and DMARC records is configuration. Moving DMARC from monitoring to quarantine and reject is enforcement. For sales and marketing teams sending cold outreach at scale, the distinction matters because an unauthenticated sequence can damage domain trust, confuse prospects, and give attackers room to impersonate your brand.

    Why Most Domains Still Get Spoofed in 2026

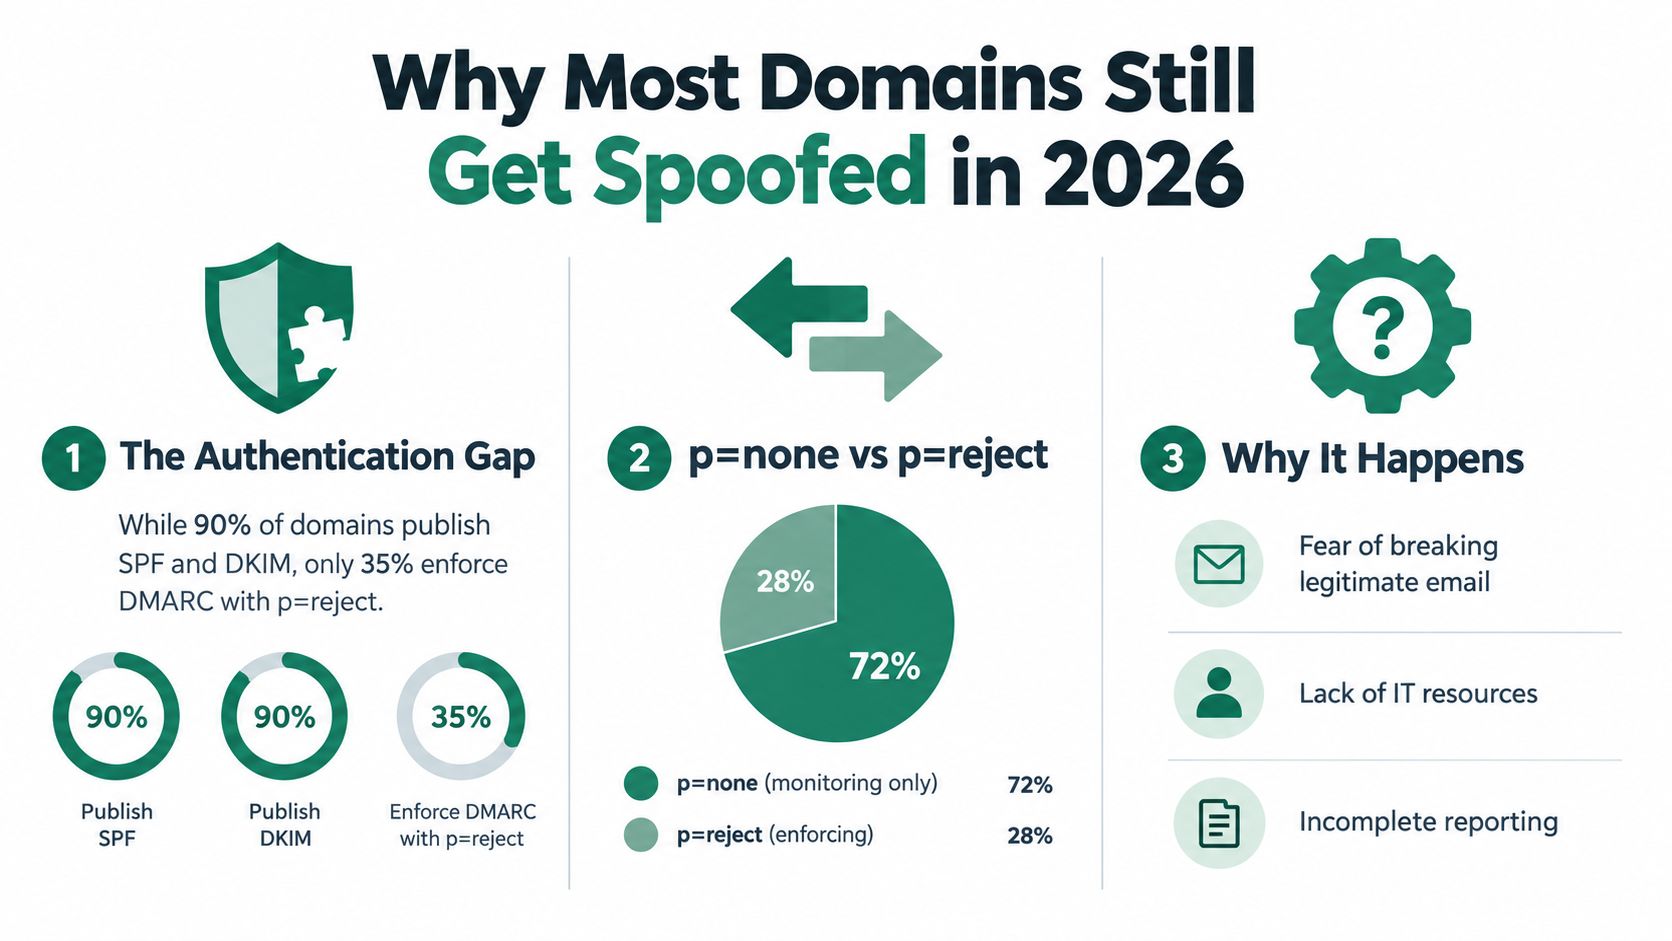
    Publishing authentication records does not stop spoofing. Enforcement does. A p=none DMARC policy provides visibility into authentication failures, but it does not tell receiving servers to quarantine or reject those messages.

    The 2026 scan of 5.5 million domains found that only 12.8% enforced an anti-spoofing policy, while 57.9% of published DMARC records remained at p=none, according to the DMARC adoption and email authentication analysis. A separate benchmark reported that 77.6% of analyzed domains weren't fully protected, including 25.8% lacking DMARC and 55.5% either missing DMARC or using p=none, as described in the UK government email security guidance.

    An infographic titled Why Most Domains Still Get Spoofed in 2026, showing statistics on email authentication practices.

    Publication isn't protection

    SPF and DKIM can authenticate legitimate messages while forged mail continues to pass through. Without DMARC alignment and an enforcement policy, attackers can place your visible domain in the From address while sending through infrastructure your records do not authorize.

    Mailbox providers also use authentication when assessing sender trust. In 2024, Google and Yahoo announced requirements for bulk senders that included SPF or DKIM and DMARC alignment for domain protection. A 2025 security summary linked those requirements to a 65% reduction in unauthenticated email, according to the Email phishing and DMARC security trends.

    Weak enforcement creates two problems. Spoofers get a clearer path to impersonation, while legitimate campaigns can receive weaker trust signals from mailbox providers.

    The operational causes

    Marketing and sales teams often delay enforcement because they fear blocking legitimate mail. That concern should trigger an inventory, not permanent monitoring. Document every marketing automation platform, CRM, transactional service, sales engagement tool, and internal application. Then align each sender before changing the policy.

    Practical rule: Treat p=none as an investigation phase, not a finished security posture.

    For outreach programs, ownership must be explicit. Each tool needs a documented sending domain, DKIM configuration, and accountable owner before a sequence launches. Monitor alignment, test enforcement in stages, and make rejection the destination. A published record without that operating discipline leaves your domain available for abuse.

    How Email Authentication Actually Works

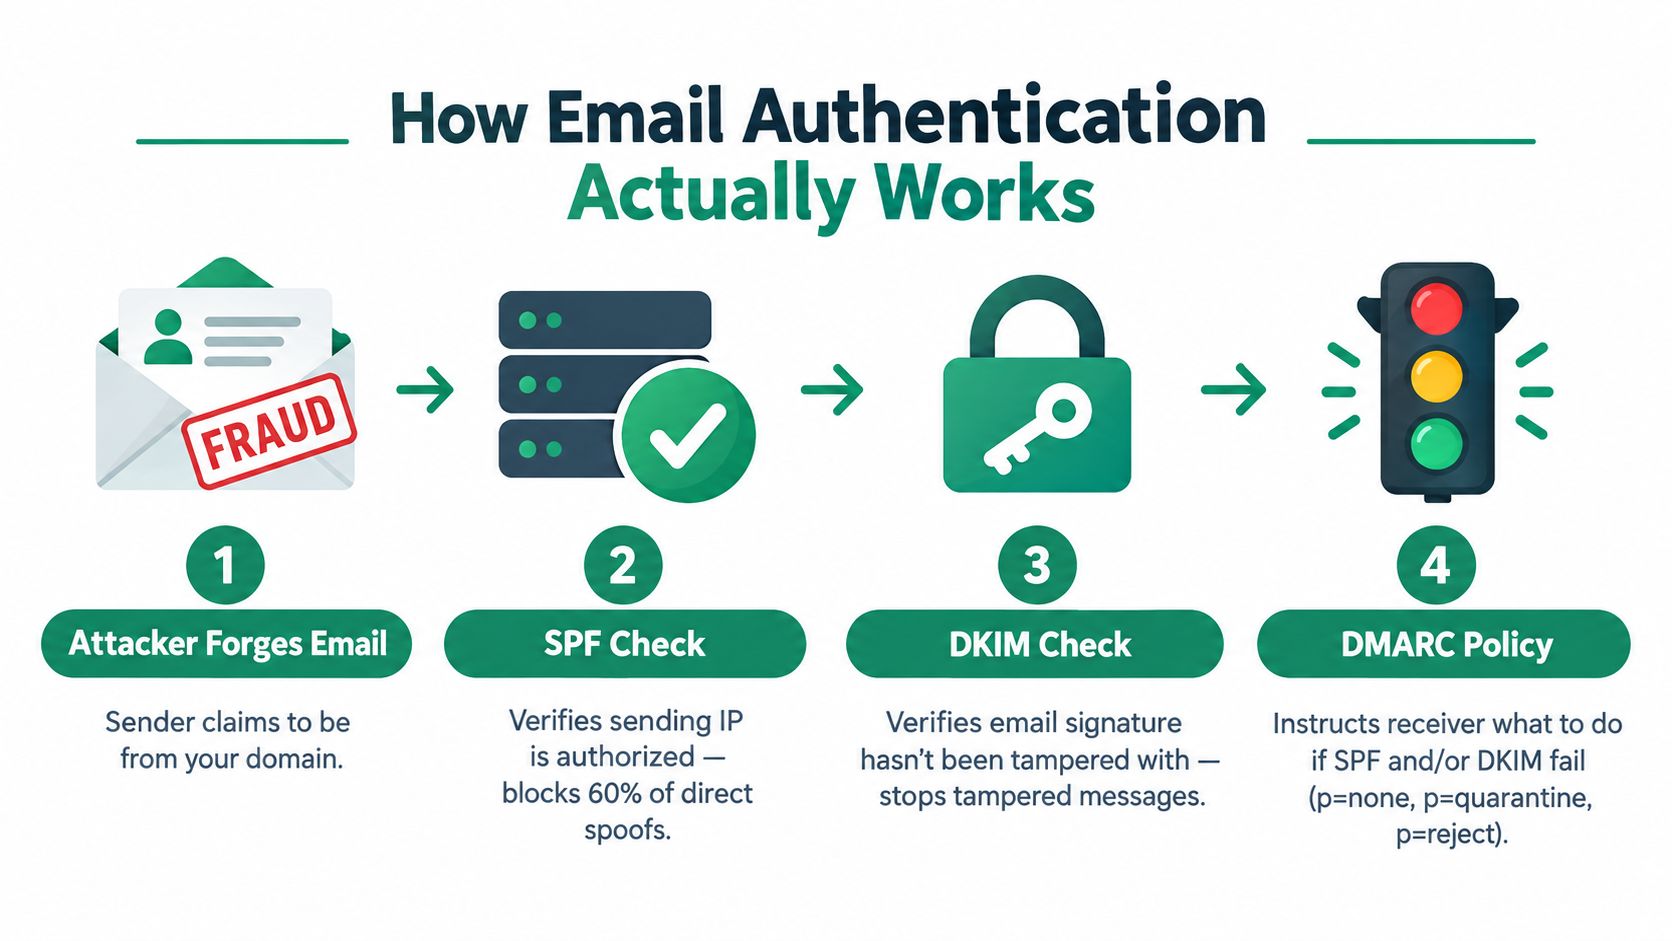
    Email authentication uses three complementary controls. SPF answers whether the sending infrastructure is authorized. DKIM proves that an authorized system signed the message and that signed content wasn't altered. DMARC connects those results to the visible From domain and tells the receiving server what to do when authentication fails.

    A diagram illustrating the four steps of email authentication including SPF, DKIM, and DMARC verification processes.

    The four-part decision

    An attacker can send a message that claims to come from your domain. The receiving server then evaluates the message through several checks:

    1. SPF check. The server examines the envelope sender domain and looks up its SPF record. That record lists authorized sending services or infrastructure. If the source isn't authorized, SPF fails.
    2. DKIM check. The receiving server finds the DKIM selector in the message, retrieves the matching public key from DNS, and verifies the cryptographic signature. A valid signature helps show that the message came through a configured sender and wasn't modified after signing.
    3. DMARC alignment. DMARC compares the authenticated SPF or DKIM domain with the domain visible to the recipient in the From address. Authentication that belongs to an unrelated vendor domain may pass SPF or DKIM but still fail DMARC alignment.
    4. Policy decision. The domain owner's DMARC policy determines whether the receiving server should monitor, quarantine, or reject the message. With p=none, the receiver reports the event without blocking it. With p=quarantine, the receiver is asked to treat the message as suspicious. With p=reject, unauthenticated mail is blocked at the mail server, which government guidance identifies as the strongest protection. (Cybersecurity and Infrastructure Security Agency phishing guidance)

    SPF and DKIM aren't interchangeable. SPF is tied to the sending path and can be affected by forwarding. DKIM travels with the message, but it doesn't by itself tell the receiving server what to do with a failure. DMARC supplies the enforcement instruction and alignment requirement.

    For a practical primer that complements the technical flow, review this email security guidance from Blowfish Technology. Teams responsible for outbound campaigns should also audit how to improve email deliverability before increasing send volume or adding another platform.

    The key is the chain. SPF authorizes infrastructure, DKIM authenticates message integrity, and DMARC turns those signals into a receiver-side action.

    Setting Up SPF and DKIM the Right Way

    Treat SPF and DKIM as enforcement controls, not DNS housekeeping. Start by listing every system allowed to send as your domain, including Google Workspace, Microsoft 365, marketing automation, transactional email, CRM notifications, Outreach, Salesloft, Instantly, and applications that send password resets or invoices. Your outreach tools belong in this inventory because an untracked sender can undermine DMARC later.

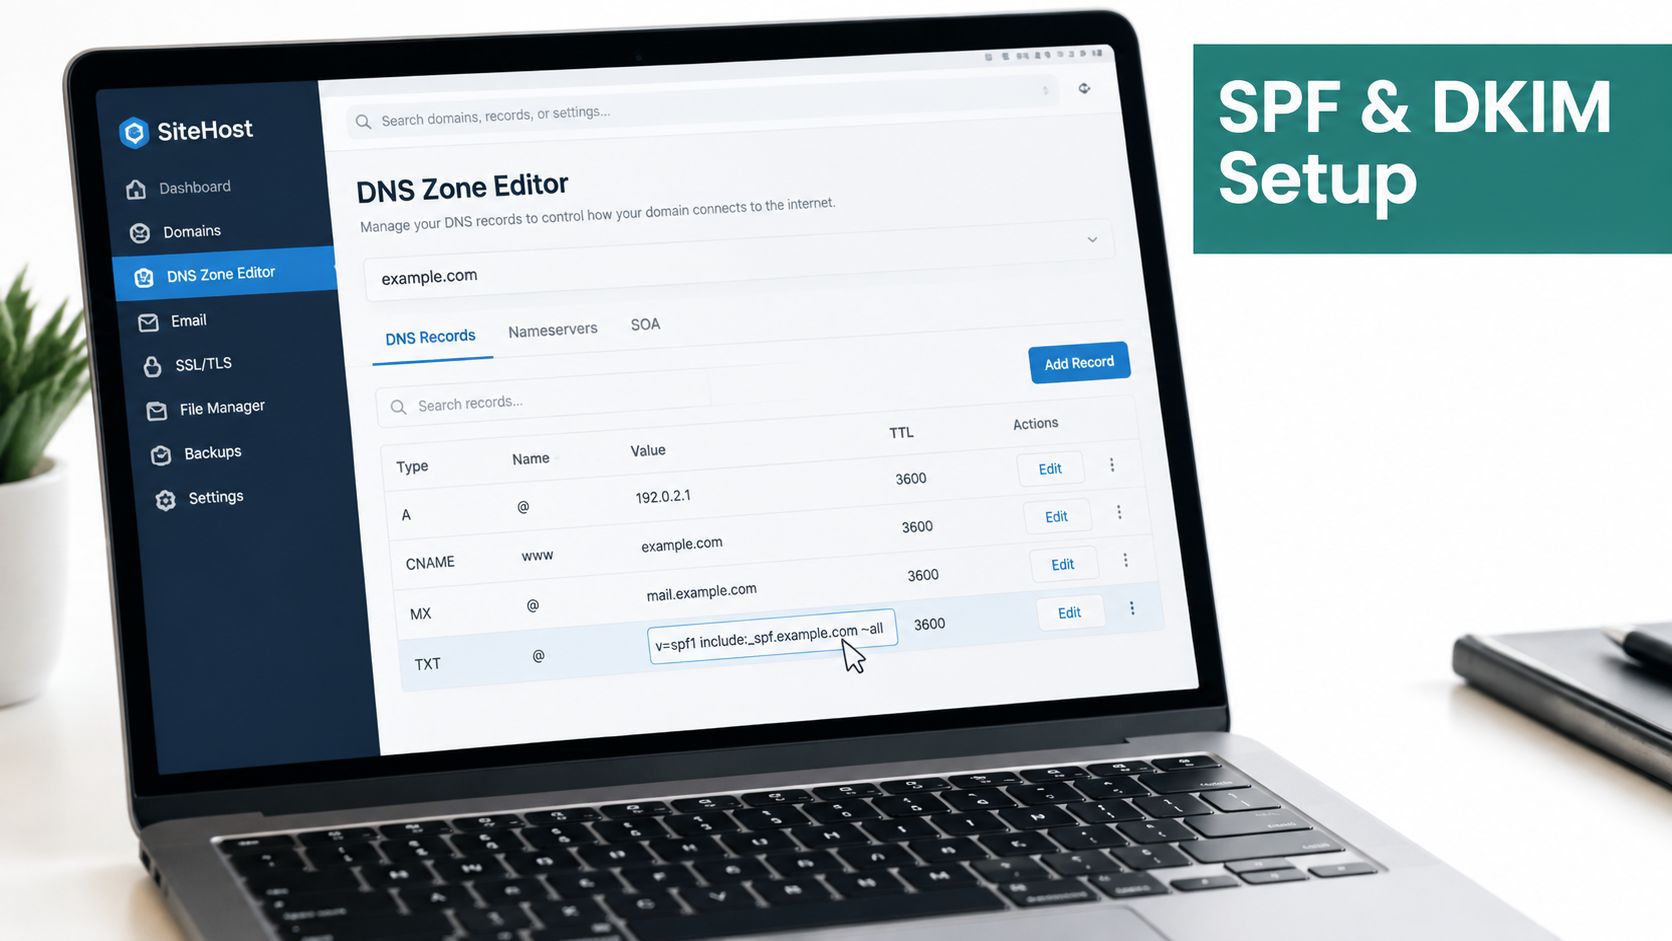
    Screenshot from https://example.com/screenshots/spf-dkim-dns-records.png

    Build the sender inventory first

    For each platform, request the current SPF include, DKIM selector, envelope-from domain, and alignment instructions from its documentation page. Do this instead of using a spreadsheet last updated before the vendor migrated to new infrastructure. Record the responsible owner and the campaigns or transactional streams that depend on the connection.

    SPF has a 10-DNS-lookup limit, so adding every vendor casually creates a failure point. (Email spoofing prevention guidance) Publish only verified senders, and finish with a hard fail:

    v=spf1 include:verified-mail-provider.example include:verified-outreach-provider.example -all

    This is a template, not a record to publish unchanged. Replace each placeholder with the vendor's documented mechanism. Do not use +all, which authorizes every sender, or ?all, which provides no useful authorization signal. Remove discontinued vendors promptly. Consolidate overlapping services where possible, and check the final record for lookup limits before saving it.

    Configure DKIM per sending platform

    Each platform should generate its own DKIM key pair or provide managed signing. Publish the public key at the specified selector, usually under selector._domainkey.yourdomain.com, then enable signing in that platform.

    For Google Workspace and Microsoft 365, generate or retrieve the configuration in the administrator console. For Outreach, Salesloft, Instantly, and similar tools, use the custom-domain authentication area. Copy the selector and record value from the service. Never reuse a selector from another account or one key across unrelated sending systems.

    Send test messages through every important stream. Inspect the receiving headers and confirm SPF passes, DKIM passes, and the authenticated domains align with the visible From address. One successful platform proves nothing about the others.

    Outbound rule: Do not move to DMARC enforcement while a legitimate sender remains unidentified or unaligned.

    Rolling Out DMARC from Monitoring to Reject

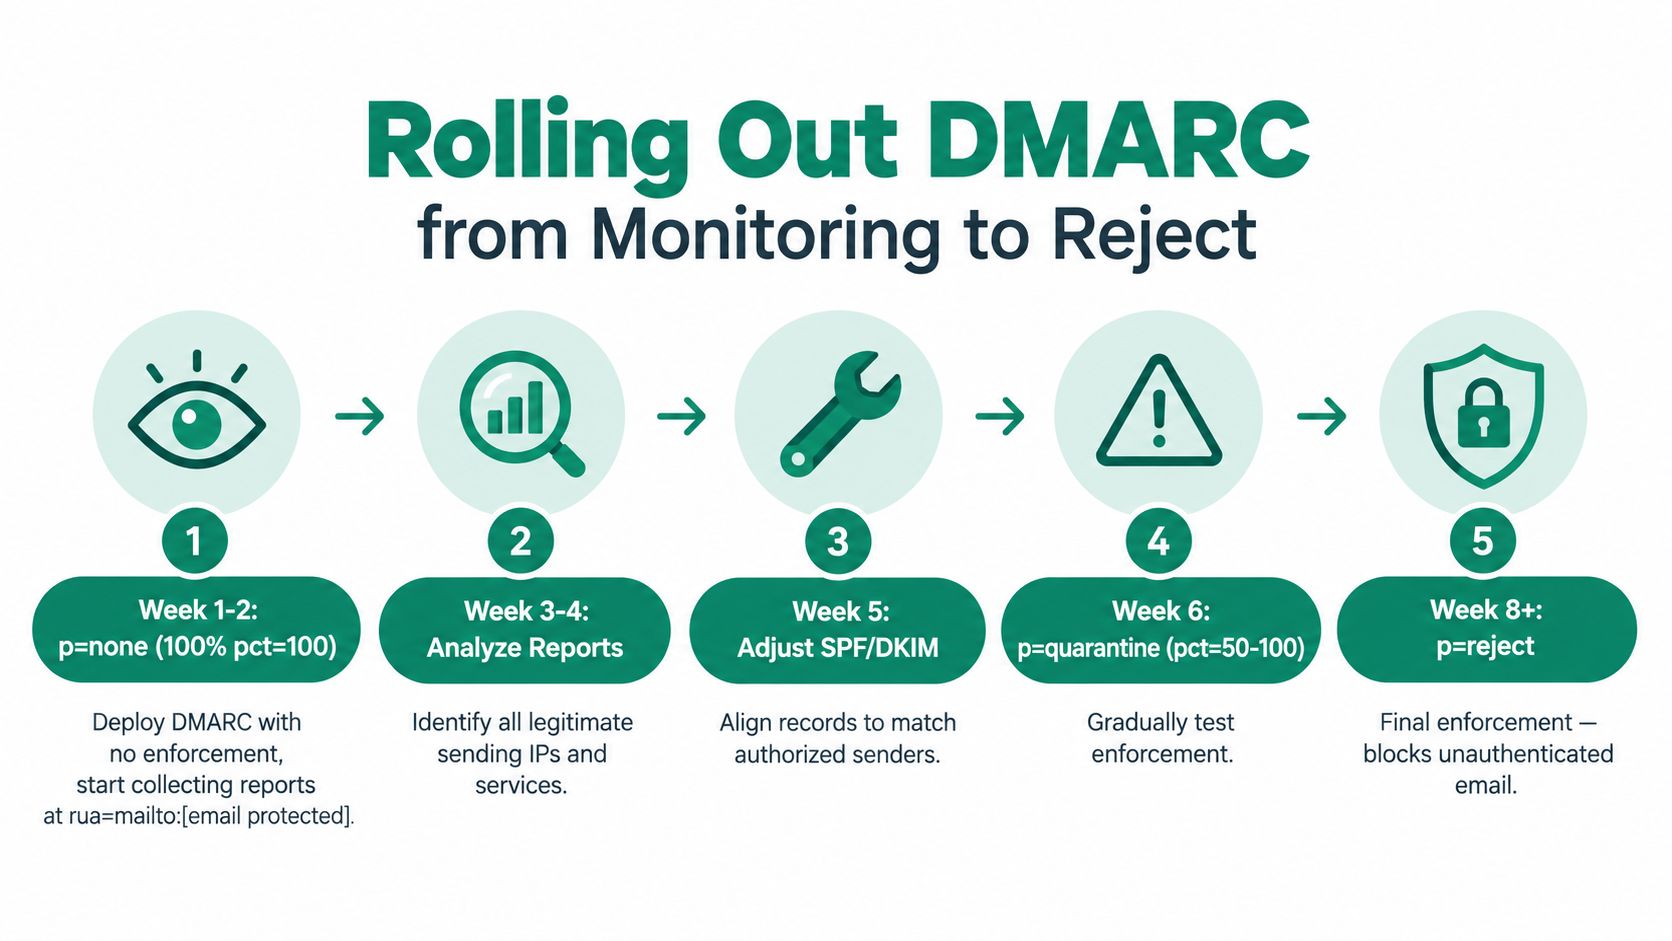
    DMARC rollout is an enforcement program, not a DNS checklist. Start by exposing every sender, fix legitimate traffic, then tighten the policy only when reports show that authorized mail will pass.

    Phase one: establish visibility

    Publish a monitoring policy with an aggregate-report mailbox:

    v=DMARC1; p=none; pct=100; rua=mailto:dmarc-reports@yourdomain.com

    Use a parser that converts aggregate XML into records your team can review. For each source, track the sending IP, SPF result, DKIM result, alignment status, and reported disposition. Compare those findings with the sender inventory. An unfamiliar source may be a forgotten CRM integration, forwarding path, vendor, or spoofing attempt.

    Assign an owner to the report stream. That person should review findings, document decisions, and contact platform administrators when a legitimate stream fails alignment. A mailbox full of reports does not protect the domain.

    Phase two: apply controlled pressure

    After legitimate sources are authenticated and aligned, move to quarantine with limited coverage:

    v=DMARC1; p=quarantine; pct=10; rua=mailto:dmarc-reports@yourdomain.com

    Increase the percentage only after validating campaign traffic, transactional messages, replies, and forwarding behavior. Use a staged rollout rather than switching the entire domain at once.

    Review these signals daily:

    • Alignment rates: Separate SPF alignment from DKIM alignment. Fix any legitimate stream that depends on only one.
    • New sources: Investigate newly reported IPs, vendors, and infrastructure before they become permanent exceptions.
    • Quarantine effects: Check spam placement and user reports for messages that should reach the inbox.
    • Subdomains: Define a policy for outreach subdomains instead of assuming the organizational domain policy is safe for every use.
    • Vendor rewriting: Confirm that each outreach platform preserves the envelope sender and signing domain required for alignment.

    Sales and marketing teams should test every sending tool under the same policy they will use in production. A sequence that passes in a staging setup can fail once the platform changes its return path or DKIM selector.

    Phase three: enforce rejection

    Move to:

    v=DMARC1; p=reject; pct=100; rua=mailto:dmarc-reports@yourdomain.com; ruf=mailto:dmarc-forensics@yourdomain.com; adkim=s; aspf=s

    Use strict alignment only for systems that support it reliably. The trigger for rejection is evidence, not a calendar date. Every legitimate sender must be identified, authenticated, aligned, tested, and monitored.

    The CISA phishing guidance identifies p=reject as the strongest DMARC protection because receiving servers can block unauthenticated messages. Keep reports flowing after enforcement. Without monitoring, a newly adopted sales tool or acquisition platform can fail.

    A five-step infographic guide illustrating the process of rolling out DMARC, from monitoring to reject.

    Hardening Beyond DMARC for Outreach Teams

    DMARC protects the authenticated domain, not the brand around it. Criminals can register lookalike domains, compromise legitimate mailboxes, or abuse trusted services. Barracuda's 2026 analysis reported spoof rates rising from 12.08% in Q2 2025 to 24.30% in Q2 2026, while ARC absence remained above 72%. It recommends layered controls, including MFA, conditional access, risky sign-in monitoring, time-of-click URL analysis, and automated response. (Barracuda 2026 email threats report)

    For cold outreach, separate sending from corporate communications. Sales sequences should not send from your primary corporate domain. Use dedicated, authenticated sending domains or subdomains, assign each platform its own DKIM identity, and document ownership. If an outreach stream develops a reputation problem, executive, support, and transactional mail should remain isolated.

    Control What it blocks Outreach-team action
    BIMI with a VMC Prevents unauthenticated messages from receiving the authenticated brand-logo treatment Meet the enforced DMARC prerequisite, prepare a compliant logo, and obtain the required certificate
    MTA-STS Helps prevent downgrade or insecure SMTP transport paths Publish a policy and move to enforcement only after testing receiving infrastructure
    TLS-RPT Reports TLS delivery and negotiation failures Send reports to a monitored security mailbox
    Null MX and restrictive SPF Prevents parked domains from becoming usable mail sources Set domains that never send or receive mail to reject inbound assumptions and authorize no senders
    PTR and abuse mailbox hygiene Reduces ambiguity around outbound ownership and incident contact Keep reverse-DNS identity and abuse reporting details current
    Lookalike-domain monitoring Detects registrations that imitate your brand Track typo patterns, register strategically, and route abuse reports quickly

    Treat MTA-STS and TLS-RPT as operating controls, not records you publish and forget. Add them to the same register as SPF, DKIM, and DMARC, with an owner, test date, report destination, and escalation path. Keep PTR records and abuse contacts current so receiving providers can identify and report problems.

    Give each outreach provider its own SPF authorization and DKIM key. Do not reuse one DKIM key across every platform. Rotate sending subdomains according to governance and reputation policy, never to evade provider controls. Before approving a tool, confirm that it supports aligned authentication, monitored reporting, and a documented shutdown process. If you are assessing managed services, use this guide to choose the right email provider.

    EmailScout can help sales and marketing teams discover contact addresses for prospecting. That workflow still requires permission, list hygiene, and authenticated sending infrastructure. Use documented email security best practices to govern access, authentication, campaign approval, and vendor use. A contact-discovery tool does not enforce domain security.

    Monitoring, Reporting, and Incident Response

    A CFO's name appears on an invoice reminder from a lookalike domain, asking a supplier to change payment details. At the same time, DMARC aggregate reports show a new source that does not align with the company's domain. The security lead has one hour to decide whether the message reflects spoofing, a compromised account, or an undocumented legitimate service.

    The first-hour response

    Begin by pulling DMARC source IPs, timestamps, and authentication results before reviewing the sender's display name.

    • Correlate reports: Compare the DMARC source IP and timestamps with outbound sending logs.
    • Classify the path: Establish whether the message came from an unauthorized server, a forwarded route, a lookalike domain, or a compromised approved account.
    • Preserve samples: Save the forensic report and complete headers where available.
    • Alert providers: Use postmaster and abuse channels for Gmail, Microsoft, and Yahoo, then report malicious infrastructure.
    • Protect recipients: Notify affected customers, suppliers, finance staff, and executives through a trusted channel.
    • Request takedowns: Submit abuse reports for the impersonating domain, hosting provider, links, and attachments.

    Read a DMARC aggregate record in sequence. The source IP identifies the reporting sender. SPF and DKIM show authentication outcomes, alignment indicates whether those results match the visible From domain, and disposition records how the receiving provider handled the message.

    Use this SMB email safety guide to support response procedures and access controls. Before sales or marketing staff engage with suspicious contacts, use a workflow for checking whether an email address is associated with spam. EmailScout can support that address-checking workflow, but it does not decide whether a message is authorized or enforce domain policy.

    Make review recurring

    Review alignment and new sending sources weekly. Triage forensic samples monthly under your privacy and retention rules. Re-audit the authentication posture quarterly, covering parked domains, outreach vendors, subdomains, DKIM selectors, MTA-STS, TLS reporting, and account access.

    After a confirmed incident, document the event and notify affected parties. Tighten the domain policy to p=reject when the sender inventory supports enforcement. Add the impersonating domain or infrastructure to your organization's blocklist and threat-intelligence feeds, then assign an owner to verify that the controls remain active.

    Your 30/60/90 Anti-Spoofing Plan

    The distance between a published DMARC record and enforced spoofing protection is operational, not technical. A team needs ownership, reporting, change control, and a clear point at which monitoring ends.

    First 30 days

    Complete the sender inventory. Publish SPF and DKIM for every legitimate system, set DMARC to p=none with an aggregate-report address, and confirm that reports reach a parser that someone reviews. Assign one owner in security or infrastructure and one partner in marketing operations.

    Days 31 through 60

    Tighten SPF with -all after validating every authorized sender. Review BIMI prerequisites, enable MTA-STS and TLS-RPT, and secure parked and typo domains with appropriate DNS and registration controls.

    Deliver a short sales-team training session covering display-name impersonation, reply-to manipulation, lookalike domains, and outreach-tool authentication. Salespeople should know that a familiar name isn't proof of a legitimate address and that payment or credential requests require separate verification.

    Days 61 through 90

    Graduate DMARC to p=quarantine for a controlled period. Escalate to p=reject; pct=100 only when aligned legitimate volume exceeds 95%, as specified in the rollout plan, and the remaining failures have documented owners and decisions. Finalize BIMI with a VMC where it fits your brand and mailbox-provider requirements, then run a tabletop spoofing drill with security, finance, marketing, sales, and customer support.

    Keep the operating rule visible in every campaign approval checklist:

    If it sends as your domain, it must authenticate, align, and be auditable.


    EmailScout helps sales and marketing teams find decision-maker email addresses and build prospecting lists, while your team remains responsible for authenticated, compliant outreach infrastructure. Visit EmailScout to support contact discovery alongside the SPF, DKIM, DMARC, and monitoring controls that protect your sending identity.

  • SPF DKIM DMARC Explained: A Complete Guide for Senders

    SPF DKIM DMARC Explained: A Complete Guide for Senders

    Your team did everything “right.” The campaign copy is solid, the segment is clean, the send went out on time, and then the inboxes barely budged while the spam folder filled up. That's usually the moment people start asking whether the problem is the subject line, the list, or the platform, but the answer is often lower in the stack: email authentication.

    SPF, DKIM, and DMARC are the three checks mailbox providers use to decide whether your message looks like a legitimate send or an impersonation attempt. Google and Yahoo's bulk-sender rules made that clearer by treating authentication as a requirement for large-scale sending, not a nice-to-have, for senders above 5,000 emails per day. Those rules also expect SPF, DKIM, and a DMARC record with at least p=none, plus alignment and one-click unsubscribe, because mailbox providers are now using authentication as part of normal inbox placement decisions as summarized in this deliverability overview.

    If you've ever added one more tool, one more CRM, or one more newsletter platform and watched deliverability wobble, you've already met the core problem. This isn't just about publishing records. It's about making sure every legitimate sender in your stack can prove who it is, and doing that without breaking mail you want delivered. For a practical companion on filtering issues, see how to avoid spam filters.

    Why Your Emails Are Landing in Spam

    The usual pattern is familiar. A marketer sees opens drop, replies slow down, and internal stakeholders start wondering if the list went bad. The campaign itself may be fine, but mailbox providers are often making a trust decision before a human ever sees the message.

    That trust decision now depends heavily on SPF, DKIM, and DMARC. SPF checks whether the sending server is on the domain's approved list, DKIM checks whether the message has a valid cryptographic signature, and DMARC checks whether those authentication results line up with the visible From domain. In other words, the three standards work together to answer a simple question, “Is this really from who it claims to be?” The authentication stack is outlined here.

    Why inbox providers care more now

    Mailbox providers have tightened the rules because spoofing and phishing abuse are constant problems. By 2024, bulk senders were no longer dealing with a soft best practice conversation. They were dealing with policy expectations that affect whether mail is accepted, filtered, or ignored.

    Practical rule: if you send at scale, authentication isn't a security extra, it's part of your delivery infrastructure.

    That's why many teams get confused when a campaign starts failing after a new tool is added. The issue usually isn't that the content suddenly became “spammy.” It's that the sender architecture changed, and the authentication setup didn't keep up. Once that happens, inbox placement becomes less predictable, because the provider is now looking for proof, not just a familiar brand name.

    The rest of the stack starts with SPF.

    What SPF Does and Why It Comes First

    An infographic explaining how SPF records work using a club bouncer analogy to show email authentication.

    A marketer can publish a new email tool, route messages through a fresh platform, and still see delivery problems if the sending path was never updated in DNS. Sender Policy Framework, or SPF, is the approved-sender list that tells receiving servers which mail systems are allowed to send for a domain. If the server that hands off the message is on that list, SPF passes. If it is not, the message starts from a position of doubt, even when the email itself is legitimate.

    The club bouncer analogy works because SPF is checking the door, not the suit. It does not care whether the message sounds persuasive or whether the brand name looks familiar. It checks whether the server at the gate is expected to be there. An infographic explaining how SPF records work using a club bouncer analogy to show email authentication.

    What the record is doing

    An SPF record lives in DNS as a TXT record. It usually begins with v=spf1, then lists the sending paths a domain authorizes, often with mechanisms such as include, ip4, and ip6, and closes with an all qualifier that tells receivers how to handle everything else. The key operational detail is that SPF authenticates the SMTP envelope sender, not the visible From address people see in the inbox.

    That split is where confusion often starts. A campaign can look like it came from your brand while the mail server is being evaluated on a separate path. SPF is checking the transport layer, not the human-facing header. That is why SPF by itself does not stop impersonation.

    The practical problem gets bigger as a stack grows. Marketing platforms, support systems, survey tools, and cloud mail services can each add another authorized sender, and the record can become difficult to maintain. SPF also has a hard ceiling of 10 DNS lookups, so a record can fail even when every tool is legitimate that operational constraint is discussed here.

    A clean SPF record gives your team a controlled starting point. It helps mailbox providers decide whether the sending server belongs, before they look at the rest of the authentication picture.

    How DKIM Cryptographically Signs Your Message

    If SPF is the guest list, DKIM is the wax seal on the letter. It shows that the sending domain signed the message and that the signed parts were not altered in transit. Email can be relayed, forwarded, and filtered before it reaches the inbox, so that integrity check matters.

    The signing process uses a private key on the sending side and a public key published in DNS. The sender signs selected headers and body content, then the receiving server fetches the public key and checks whether the signature still matches. If the content changed, the signature fails. If the signature matches, the message can be trusted as intact from that signing domain.

    A diagram illustrating the DKIM process of cryptographically signing and verifying email messages for sender authentication.

    Why this matters for marketers

    DKIM is the part that often survives when SPF does not. Forwarding, relaying, and some intermediate systems can break SPF because the sending path changes. DKIM can still pass if the signed headers and body stay intact, so deliverability teams treat it as a resilience layer, not just a record to publish.

    The headers matter too. Signing the right headers, especially the ones tied to the visible identity of the message, helps receivers connect the email back to the domain that owns it. Without that connection, the message may still go out, but it loses trust signals along the way.

    This integrity model is described in the protocol overview.

    Where DMARC Fits in the Authentication Stack

    DMARC is the policy layer. SPF and DKIM answer questions about authorization and integrity, but DMARC answers the operational question, “What should receivers do if something doesn't line up?” It does that by requiring alignment, which means the authenticated domain has to match the visible From domain in a way DMARC accepts the policy framework is described by DMARC.org.

    That alignment rule is the part many teams miss. A pass on SPF or DKIM by itself isn't enough if the authenticated identifier doesn't align with the sender people see. DMARC turns authentication from a passive check into an enforceable policy.

    The policy progression that keeps mail alive

    Start with p=none, which tells receivers to monitor and report without taking enforcement action. Once the reports show that all legitimate senders are aligned, move to p=quarantine, then eventually p=reject. That staged rollout is the operational norm because it avoids breaking good mail while you're still discovering every sender in the environment Cisco's deployment guidance follows this pattern.

    DMARC also introduces reporting. The rua address is used for aggregate reports, which show you how your domain is being used at a high level. The ruf address is for forensic-style feedback where receivers support it. Those reports are the visibility layer that helps you find unauthorized senders and misconfigured systems before enforcement gets strict.

    DMARC doesn't magically stop spoofing everywhere on the internet. It gives domain owners a say in what happens when mail fails policy, and it gives them data to act on. That distinction matters, because the hard part is not publishing a record, it's learning how your real sender ecosystem behaves.

    How SPF, DKIM and DMARC Work Together

    A common failure story looks like this. A marketing team adds a webinar platform, a CRM, and a support desk, then email starts behaving unevenly. Some messages land in inboxes, some go to spam, and a few fail outright. The reason is usually not one broken record. It is a sender stack that no longer matches how mail is being sent.

    SPF verifies which servers are allowed to send for your domain at the envelope level. DKIM verifies that the message content has not been changed after it was signed. DMARC compares those results with the domain in the visible From address and decides whether the message should pass, be watched, or be blocked. The three records work like linked checkpoints in a workflow, each one answering a different question about the same email.

    Aspect SPF DKIM DMARC
    What it authenticates The sending server at the SMTP envelope level Message integrity through a cryptographic signature Whether authentication aligns with the visible From domain
    What it ignores The visible From header The sending server path Nothing, it evaluates the combined result and policy
    Typical weakness Can fail with forwarding or relays Can fail if headers or body are altered Depends on SPF or DKIM being set up correctly
    Operational role Authorizes infrastructure Protects the message itself Enforces policy and reporting

    A workflow view makes the relationship clearer. Mail leaves your system, SPF checks whether the server belongs on the approved list, DKIM seals the content so receivers can detect tampering, and DMARC checks whether the authenticated identity matches the brand name the recipient sees. If a vendor sends through its own infrastructure, or a forwarding service rewrites the path, SPF may fail even though the email was legitimate. If a help desk tool changes the message after signing, DKIM may fail even though the sender was authorized. DMARC sits on top of both outcomes and asks whether the domain identity still lines up.

    That alignment step is where real-world surprises show up. A team can have SPF passing for one platform and DKIM passing for another, yet DMARC still fails because the authenticated domain belongs to a subdomain the policy does not recognize, or because a new tool was never added to the sender inventory. Before tightening policy, audit every system that sends mail in your name, compare it against DMARC reports, and confirm which platforms rely on SPF, which sign with DKIM, and which need both to stay aligned. That review catches the quiet problems that simple record-by-record explanations miss.

    Bottom line: SPF, DKIM, and DMARC only make sense as a sender system. The real work is keeping every legitimate mail source aligned as your stack changes.

    Common Misconfigurations and How to Fix Them

    Most authentication failures come from sender sprawl, rushed setup, or the assumption that one record will cover every service forever. That rarely holds once a team starts using multiple CRMs, automation tools, help desks, and cloud mail platforms. The records may look fine on paper, while the actual sender chain has already drifted.

    The failures that show up most often

    • SPF lookup limit exceeded. Add enough third-party senders and the record becomes too complex for receivers to evaluate cleanly. The fix is to review every legitimate sender, remove unused services, and restructure the record so it stays within the lookup ceiling.
    • DKIM not enabled everywhere. Some platforms sign by default, while others need manual activation. The fix is to confirm each sending platform is signing outbound mail with the right selector and key, then test a real message instead of trusting the dashboard alone.
    • Alignment failure. A service may authenticate, yet the authenticated domain still does not match the visible From domain. The fix is to align the sending identity with the brand domain or subdomain that DMARC expects, so the recipient sees the same domain family that is being validated.
    • DMARC published too aggressively. Teams sometimes jump to rejection before they know all the mail streams. Start with p=none, inspect reports, then tighten policy gradually after you can account for the legitimate sources.
    • Forwarded mail failing SPF. Forwarding changes the sending path, so SPF can break even when the original message was legitimate. The fix is to rely on DKIM where possible and review how forwarding services handle authenticated mail.

    The main lesson is that SPF becomes less useful as a standalone trust signal once the sender architecture grows. It still matters, but it cannot carry the whole job by itself. DMARC depends on alignment and at least one passing path, so the task is designing a sender ecosystem that can expand without creating false failures, as noted earlier in this scaling issue is covered in the SPF/DKIM/DMARC explainer.

    A rushed setup often feels fine on day one and breaks later when someone adds one more tool. The fix is usually architectural, not cosmetic. Audit every system that sends mail in your name, compare it against DMARC reports, and keep tightening only after the legitimate flows are clearly mapped.

    Verifying Your Setup With Free Tools

    You don't need a terminal-heavy security workflow to check whether your setup is working. Start by looking up the published authentication records with a DNS lookup tool, then compare what you find to the headers on a real message. If the records are published but the headers show failures, the problem is usually in alignment or platform configuration, not DNS syntax.

    MXToolbox is useful for quick SPF and DKIM checks, and Gmail's raw message view is still one of the best ways to inspect Authentication-Results. A passing line will show SPF=pass, DKIM=pass, and DMARC=pass together when everything lines up. If one passes and another fails, that's a clue about where the sender chain is breaking.

    For a marketer-friendly walkthrough of message validation, see how to verify emails.

    What to look for in the header

    • SPF pass with the right domain. Confirms the sending server was expected.
    • DKIM pass with the right signing domain. Confirms the message stayed intact.
    • DMARC pass with alignment. Confirms the visible From domain matches the authenticated identity.

    Gmail Postmaster Tools is worth connecting once the domain is live. It helps you watch domain reputation patterns at scale, which is especially useful when multiple teams are sending from the same brand domain. If deliverability dips after a new launch, you can compare the timing against authentication changes instead of guessing.

    A Phased Plan for Sales and Marketing Teams

    A good rollout is boring in the best way. Days 1 to 30 are for inventorying every sender, publishing SPF and DKIM, and putting DMARC p=none in place with aggregate reports enabled. Days 31 to 60 are for reading those reports, fixing alignment issues, and removing senders nobody uses anymore.

    Days 61 to 90 are where enforcement starts to make sense. Move from monitor mode into quarantine, then toward reject once the legitimate mail streams are stable and the reports are quiet. If you're preparing cold outreach or lifecycle campaigns, pair that work with a structured warm-up process and a controlled ramp like the one described in warm-up email guidance.

    The point isn't to “finish DMARC.” The point is to make authentication part of the way your team sends mail, so scaling outreach doesn't keep reintroducing risk.


    If you want a practical way to keep outbound prospecting from fighting your authentication setup, use EmailScout to build cleaner outreach lists while your sending domain gets properly aligned, then bring the whole stack under one deliverability review before your next big campaign.